Cybersecurity Regulatory Landscape 2026: 4 Key Changes Affecting Small and Medium Businesses (RECENT UPDATES, FINANCIAL IMPACT)
In an increasingly digital world, the cybersecurity threat landscape is evolving at an unprecedented pace. For Small and Medium Businesses (SMBs), staying abreast of these changes, particularly in the realm of cybersecurity regulations 2026, is not just good practice—it’s a matter of survival. Non-compliance can lead to hefty fines, reputational damage, and even business closure. As we approach 2026, several significant regulatory shifts are on the horizon, promising to reshape how SMBs manage their digital defenses. This comprehensive guide will delve into four key changes, explore recent updates, and outline the financial impact and strategic adjustments necessary for effective compliance.
The Evolving Threat Landscape and the Need for New Cybersecurity Regulations 2026
Before we dive into the specifics of cybersecurity regulations 2026, it’s crucial to understand the driving forces behind these changes. Cyberattacks are becoming more sophisticated, frequent, and targeted. SMBs, often perceived as having weaker defenses than larger enterprises, are increasingly becoming prime targets. From ransomware attacks that cripple operations to data breaches that expose sensitive customer information, the risks are substantial. Governments and regulatory bodies worldwide are responding by strengthening existing laws and introducing new ones to protect consumers, critical infrastructure, and national security. These regulations aim to establish a baseline for cybersecurity hygiene, enforce accountability, and foster a more resilient digital ecosystem.
The push for new cybersecurity regulations 2026 is also fueled by the increasing interconnectedness of global economies. Supply chain attacks, where a weakness in a smaller vendor’s security is exploited to compromise a larger organization, have highlighted the need for a holistic approach to cybersecurity. This means that even if your business doesn’t directly handle highly sensitive data, your partners’ and customers’ data security might depend on your compliance. Therefore, understanding and proactively addressing these regulatory changes is paramount for any SMB looking to thrive in the coming years.
Key Change 1: Enhanced Data Privacy and Protection Frameworks
One of the most significant areas of development in cybersecurity regulations 2026 concerns data privacy and protection. Building on the foundations laid by GDPR and CCPA, new frameworks are emerging that will demand even greater transparency, accountability, and user control over personal data. These regulations are not just about preventing data breaches but also about how data is collected, processed, stored, and shared.
Recent Updates and Global Harmonization Efforts
While GDPR (General Data Protection Regulation) in Europe and CCPA (California Consumer Privacy Act) in the US have set high standards, other regions are catching up or introducing their own stringent laws. We are seeing a trend towards global harmonization, where principles of data minimization, purpose limitation, and individual rights (such as the right to access, rectify, and erase data) are becoming universal. By 2026, expect to see more countries adopting similar comprehensive data protection acts, often with extraterritorial reach, meaning they apply to any business handling the data of their citizens, regardless of the business’s physical location.
For instance, recent updates indicate a potential federal privacy law in the United States, which could consolidate the patchwork of state-level regulations. This would simplify compliance for businesses operating across state lines but likely introduce new, more demanding requirements. Similarly, in Asia and Latin America, new data protection laws are being enacted and revised, often mirroring the robust provisions of GDPR.
Financial Impact on SMBs
The financial impact of enhanced data privacy regulations on SMBs can be substantial. Compliance often requires:
- Legal Consultation: Engaging lawyers to interpret complex regulations and update privacy policies.
- Technology Upgrades: Investing in data encryption, access control systems, and data loss prevention (DLP) solutions.
- Training: Educating employees on data handling best practices and privacy awareness.
- Data Mapping and Inventory: Identifying where personal data is stored, how it flows, and who has access to it.
- Data Protection Officer (DPO): Depending on the size and nature of the business, appointing a DPO might become mandatory.
Fines for non-compliance can be crippling, often calculated as a percentage of global annual turnover or a fixed maximum amount, whichever is higher. For SMBs, even a single significant fine could lead to bankruptcy. Therefore, early preparation and investment are crucial to mitigate these risks.
Key Change 2: Stricter Breach Notification Requirements
Data breaches are an unfortunate reality of the digital age. However, the way businesses respond to them is increasingly regulated. Cybersecurity regulations 2026 will likely introduce even stricter and more standardized breach notification requirements, impacting the timeline, scope, and content of disclosures.
Recent Updates and the Drive for Transparency
Currently, breach notification laws vary significantly by jurisdiction, creating a complex web for businesses operating internationally. The trend for 2026 is towards shorter notification windows (e.g., 72 hours from discovery), more detailed information required in the notification, and broader definitions of what constitutes a reportable breach. Regulators are pushing for greater transparency to allow affected individuals to take protective measures promptly and to hold organizations accountable for their security lapses.
Recent legislative proposals often include requirements for notifying not only affected individuals but also relevant regulatory bodies and, in some cases, the public. There’s also an increased focus on the content of these notifications, mandating clear, unambiguous language about the nature of the breach, the types of data compromised, and the steps the organization is taking to mitigate harm and prevent recurrence.
Financial Impact on SMBs
The financial implications of stricter breach notification requirements for SMBs extend beyond potential fines:
- Incident Response Planning: Developing and regularly testing robust incident response plans is critical. This involves legal, technical, and communication expertise.
- Forensic Investigations: The immediate need to conduct thorough forensic investigations to understand the scope and cause of a breach can be costly.
- Communication Costs: Notifying affected individuals can involve significant expenses for postage, call centers, and public relations firms.
- Credit Monitoring: Offering credit monitoring services to affected individuals for a certain period is often a requirement, adding to the financial burden.
- Reputational Damage: While not a direct financial cost, the long-term impact of reputational damage can lead to lost customers, reduced revenue, and difficulty attracting new talent.
Proactive investment in cybersecurity measures that prevent breaches in the first place, along with a well-rehearsed incident response plan, will be far more cost-effective than dealing with the aftermath of a poorly managed breach.
Key Change 3: Increased Focus on Supply Chain Cybersecurity
The vulnerability of supply chains has become a major concern for governments and businesses alike. As organizations increasingly rely on third-party vendors, software, and services, the security posture of these external entities directly impacts the overall security of the primary organization. Cybersecurity regulations 2026 will place a much stronger emphasis on securing the entire supply chain, making SMBs accountable for the security practices of their vendors.
Recent Updates and Vendor Risk Management
Recent high-profile supply chain attacks, such as the SolarWinds incident, have highlighted the catastrophic consequences of neglecting vendor security. Consequently, new regulations are emerging that mandate more rigorous vendor risk management programs. This includes conducting due diligence on third-party providers, requiring specific security clauses in contracts, and even auditing vendors’ security controls.
For instance, the US government’s executive orders on cybersecurity are pushing for enhanced software supply chain security, including requirements for software bill of materials (SBOMs) and secure software development practices. Similar initiatives are gaining traction globally, indicating that by 2026, SMBs will need to demonstrate not only their own cybersecurity resilience but also the resilience of their entire digital supply chain.
The cost of a compromised supply chain can far outweigh the investment in proactive vendor risk management. SMBs must recognize that their security is intrinsically linked to the security of their partners.
Financial Impact on SMBs
Addressing supply chain cybersecurity will introduce several financial considerations for SMBs:
- Vendor Assessment Tools: Investing in tools and services to assess and monitor the cybersecurity posture of third-party vendors.
- Contractual Revisions: Legal costs associated with updating vendor contracts to include stringent cybersecurity requirements and liability clauses.
- Enhanced Due Diligence: Allocating resources for more thorough due diligence processes when onboarding new vendors.
- Security Audits: Potentially funding or participating in security audits of critical vendors.
- Internal Process Changes: Redesigning procurement and vendor management processes to integrate cybersecurity considerations from the outset.
Key Change 4: Mandatory Cybersecurity Framework Adoption and Audits
Beyond specific data privacy or breach notification rules, there’s a growing trend towards mandating the adoption of recognized cybersecurity frameworks and undergoing regular audits. This aims to provide a structured approach to cybersecurity management and ensure continuous improvement. Cybersecurity regulations 2026 will likely see an increase in sectors and sizes of businesses required to adhere to such frameworks.
Recent Updates and Framework Consolidation
Frameworks like NIST Cybersecurity Framework, ISO 27001, and CIS Controls provide comprehensive guidelines for managing cybersecurity risks. While historically voluntary for many SMBs, these frameworks are increasingly being integrated into regulatory requirements. Some recent updates indicate that certain industries (e.g., critical infrastructure, healthcare, finance) are already facing mandatory adoption, and this scope is expected to broaden significantly by 2026.
Furthermore, there’s a drive towards consolidating and harmonizing these frameworks, making it easier for businesses to comply with multiple regulations by adhering to a single, robust framework. Regulators are also beginning to mandate independent third-party audits to verify compliance, moving beyond self-attestation.
Financial Impact on SMBs
Adopting a cybersecurity framework and undergoing audits will have several financial implications for SMBs:
- Implementation Costs: Significant investment in resources (personnel, technology, training) to implement the controls outlined in the chosen framework.
- Consulting Services: Hiring cybersecurity consultants to guide the implementation process and ensure proper alignment with the framework.
- Audit Fees: Regular costs associated with independent third-party audits to verify compliance.
- Continuous Improvement: Ongoing investment in maintaining and improving the cybersecurity posture to meet evolving framework requirements.
- Staffing: Potentially hiring dedicated cybersecurity staff or upskilling existing IT personnel to manage the framework’s requirements.
While the initial investment might seem daunting, adopting a robust framework is often the most effective way to achieve and maintain compliance across various regulations, ultimately reducing the overall risk and cost of managing cybersecurity.
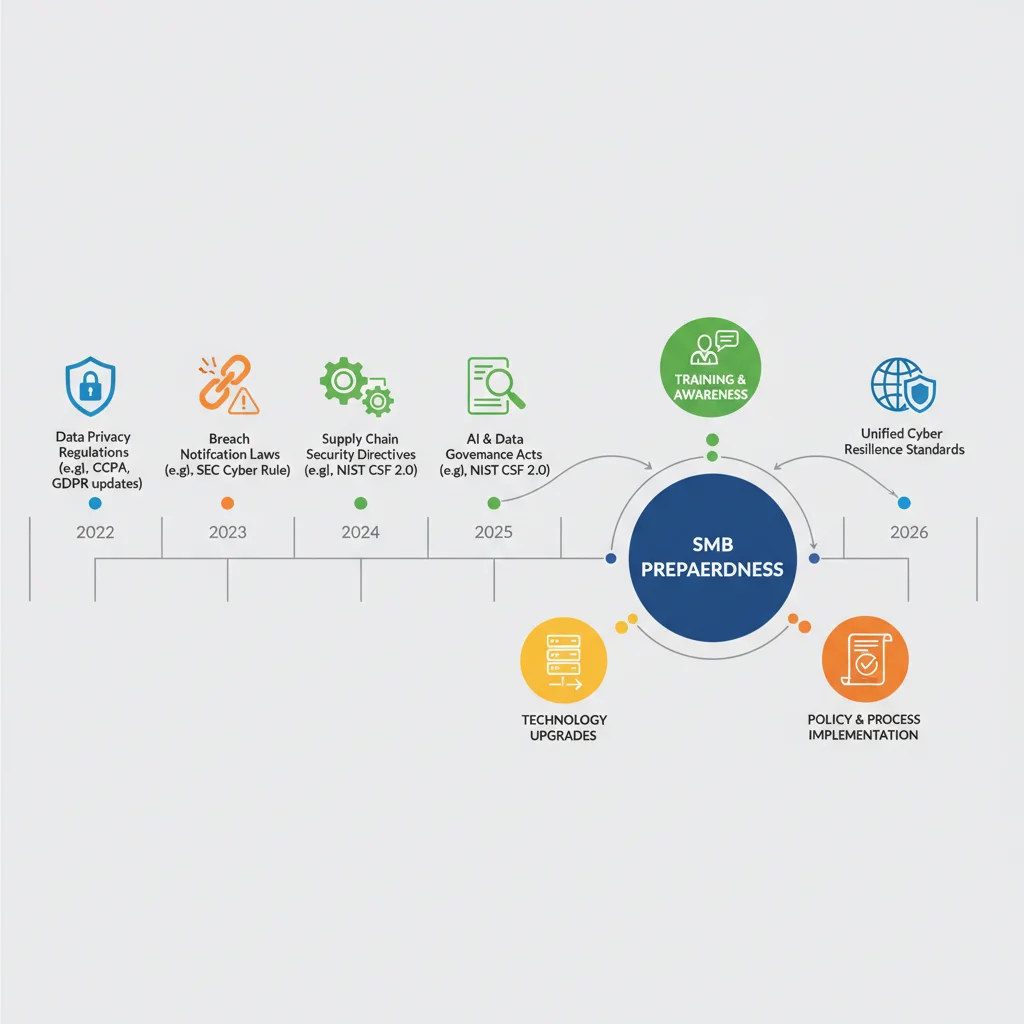
Preparing Your SMB for Cybersecurity Regulations 2026: Actionable Steps
The prospect of new cybersecurity regulations 2026 can seem overwhelming for SMBs with limited resources. However, proactive preparation is key to turning potential challenges into opportunities for growth and resilience. Here are actionable steps your business can take:
1. Conduct a Comprehensive Risk Assessment
Understand your current cybersecurity posture, identify critical assets, and pinpoint vulnerabilities. This assessment should cover your data, systems, and processes. Knowing where your weaknesses lie is the first step toward strengthening your defenses and aligning with future regulatory requirements.
2. Stay Informed and Seek Expert Advice
The regulatory landscape is dynamic. Regularly monitor updates from relevant government bodies and industry associations. Consider engaging cybersecurity and legal experts who specialize in compliance. Their insights can help you navigate complex regulations and tailor strategies to your specific business needs.
3. Invest in Foundational Cybersecurity Measures
Many new regulations build upon basic cybersecurity hygiene. Ensure you have strong access controls, multi-factor authentication (MFA), regular data backups, endpoint protection, and a robust firewall. These foundational measures not only improve your security but also lay the groundwork for easier compliance.
4. Develop and Test an Incident Response Plan
A well-defined and regularly tested incident response plan is crucial for managing breaches effectively and meeting notification requirements. This plan should outline roles, responsibilities, communication protocols, and steps for containment, eradication, recovery, and post-incident analysis. Practice drills can identify gaps before a real incident occurs.
5. Prioritize Employee Training and Awareness
Your employees are often the first line of defense. Implement continuous cybersecurity awareness training to educate them about common threats (e.g., phishing, social engineering) and their role in maintaining data security. A security-aware workforce is a significant asset in achieving compliance.
6. Embrace a Culture of Security
Cybersecurity should not be seen as just an IT function but as a core business imperative. Foster a culture where security is everyone’s responsibility, from the top down. Regular communication, clear policies, and leadership commitment can drive this cultural shift.
7. Review and Secure Your Supply Chain
Identify all third-party vendors and services that handle your data or connect to your systems. Assess their security practices, include strong cybersecurity clauses in contracts, and consider regular security reviews. Demand transparency from your vendors regarding their security controls.
8. Budget for Compliance Costs
Proactively allocate budget for technology upgrades, legal consultations, training, and potential audit fees. Integrating these costs into your financial planning will prevent unexpected expenditures and ensure a smoother transition to compliance with cybersecurity regulations 2026.
9. Consider Cybersecurity Insurance
While not a substitute for robust security, cybersecurity insurance can help mitigate the financial impact of a breach, covering costs such as forensic investigations, legal fees, notification expenses, and business interruption. Ensure your policy aligns with potential regulatory fines and liabilities.
10. Document Everything
Maintain thorough documentation of your cybersecurity policies, procedures, risk assessments, training records, and incident response activities. This documentation is vital for demonstrating compliance during audits and investigations.
The Opportunity in Compliance
While the new cybersecurity regulations 2026 may present challenges, they also offer significant opportunities for SMBs. Achieving compliance can enhance your reputation, build trust with customers and partners, and provide a competitive advantage. Businesses that demonstrate a strong commitment to data security are more likely to attract and retain clients in an increasingly privacy-conscious market.
Moreover, the process of complying with these regulations often leads to an overall strengthening of internal processes, improved operational efficiency, and a better understanding of your business’s digital footprint. It forces organizations to adopt best practices that ultimately make them more resilient against a wide array of threats, not just those covered by specific regulations.
Conclusion
The cybersecurity regulatory landscape is undergoing a profound transformation, with 2026 marking a critical juncture for SMBs. The four key changes—enhanced data privacy, stricter breach notification, increased focus on supply chain security, and mandatory framework adoption—will collectively demand a more proactive and sophisticated approach to cybersecurity. Understanding these recent updates and their potential financial impact is the first step toward effective preparation.
By taking actionable steps now, such as conducting risk assessments, investing in foundational security, training employees, and securing your supply chain, SMBs can not only achieve compliance with cybersecurity regulations 2026 but also build a stronger, more resilient, and trustworthy business for the future. Don’t wait until it’s too late; start preparing today to safeguard your operations and ensure long-term success in the digital economy.