Mastering 2026 Federal Data Privacy Act: Essential Business Compliance Guide
Navigating the 2026 Federal Data Privacy Act: 5 Key Compliance Changes Businesses Must Implement Now
The digital landscape is constantly evolving, and with it, the imperative for robust data protection. As we inch closer to 2026, a monumental shift is on the horizon for businesses operating within the United States: the implementation of the new federal data privacy act. This landmark legislation is poised to standardize data privacy regulations across states, presenting both challenges and opportunities for companies of all sizes. For years, businesses have grappled with a patchwork of state-specific laws, leading to complexity and inconsistency. The forthcoming federal data privacy act aims to streamline these requirements, establishing a unified framework that will fundamentally alter how personal data is collected, processed, stored, and shared.
Understanding and preparing for these changes is not merely a matter of legal obligation; it is a strategic imperative. Non-compliance could result in severe financial penalties, reputational damage, and a loss of customer trust. Conversely, proactive adaptation can enhance customer relationships, foster innovation, and position your business as a leader in data stewardship. This comprehensive guide will delve into five critical compliance changes brought about by the 2026 federal data privacy act, offering actionable insights and strategies to ensure your business is not just compliant, but thrives in this new regulatory environment.
From redefining personal data to empowering consumer rights and mandating stricter security protocols, the act touches every facet of data management. We will explore the nuances of these changes, provide practical steps for implementation, and highlight the importance of integrating data privacy into your core business operations. The time to act is now. By understanding these key shifts and developing a robust compliance strategy, your business can confidently navigate the complexities of the 2026 federal data privacy landscape.
1. Expanded Definition of Personal Data and Its Implications
One of the foundational changes introduced by the 2026 federal data privacy act is a significantly expanded definition of what constitutes ‘personal data.’ Historically, personal data might have been narrowly interpreted to include obvious identifiers like names, addresses, and social security numbers. However, the new act adopts a much broader perspective, encompassing a wider array of information that, directly or indirectly, can identify an individual. This includes, but is not limited to, IP addresses, device identifiers, geolocation data, biometric information, browsing history, and even inferences drawn from other data points that could be used to profile an individual. This expanded scope is a direct response to the sophistication of modern data collection and analysis techniques, acknowledging that seemingly anonymous data can often be re-identified or used to track individuals.
For businesses, this broader definition has profound implications. It means that many types of data previously considered non-personal, or at least less sensitive, will now fall under the stringent protections of the federal data privacy act. Companies must undertake a thorough data mapping exercise to identify all data elements they collect, process, and store that could now be classified as personal data. This involves not only direct identifiers but also indirect ones and pseudonymous data that, when combined, could lead to identification. Understanding this expanded scope is the first crucial step towards compliance. It requires a fundamental re-evaluation of data inventories, data flows, and data retention policies.
What Businesses Need to Do:
- Conduct a Comprehensive Data Inventory: Meticulously document all types of data collected, where it originates, where it is stored, who has access to it, and for what purpose it is used. This inventory must be dynamic and updated regularly.
- Re-evaluate Data Classification: Update internal data classification policies to align with the new, broader definition of personal data. Train employees on what constitutes personal data under the federal data privacy act.
- Assess Third-Party Data Sharing: Review all agreements with third-party vendors, partners, and service providers to ensure they understand and comply with the expanded definition when handling data on your behalf. Explicitly define data types and responsibilities in contracts.
- Implement Data Minimization Principles: Where possible, reduce the collection and retention of personal data to only what is strictly necessary for legitimate business purposes. This inherently lowers the risk profile.
The expanded definition is not just a technicality; it’s a philosophical shift towards greater individual control over digital footprints. Businesses that embrace this shift by understanding and acting on the new scope of personal data will be better positioned to build trust with their customers and navigate the complexities of the 2026 federal data privacy landscape.
2. Enhanced Consumer Rights: Access, Deletion, and Correction
A cornerstone of the 2026 federal data privacy act is the significant empowerment of consumer rights regarding their personal data. Building on principles seen in GDPR and CCPA, the federal act establishes a robust set of rights that individuals can exercise, compelling businesses to be more transparent and responsive in their data handling practices. These rights include, but are not limited to, the right to access personal data, the right to request deletion of personal data, and the right to correct inaccurate personal data. Furthermore, individuals will likely have the right to opt-out of the sale or sharing of their data for targeted advertising and potentially the right to data portability, allowing them to receive their data in a structured, commonly used, and machine-readable format.
For businesses, this means a substantial increase in the volume and complexity of consumer requests. It’s no longer sufficient to simply have a privacy policy; companies must establish clear, accessible, and efficient mechanisms for individuals to submit and track their requests. This requires not only technological solutions but also well-defined internal processes and adequately trained staff to handle these requests within specified timeframes. Failure to respond promptly and accurately can lead to non-compliance fines and erode customer trust, making these enhanced consumer rights a critical area for immediate attention under the new federal data privacy regulations.
What Businesses Need to Do:
- Develop Robust Request Mechanisms: Implement user-friendly portals, dedicated email addresses, or toll-free numbers for individuals to submit data access, deletion, and correction requests. Ensure these methods are clearly communicated in your privacy policy.
- Establish Internal Response Procedures: Create clear, documented workflows for receiving, verifying, processing, and responding to consumer requests within the stipulated deadlines (e.g., 30 or 45 days, as the act specifies).
- Verify Consumer Identity: Implement secure and reasonable methods to verify the identity of individuals making requests to prevent unauthorized access or deletion of data.
- Map Data for Easy Retrieval/Deletion: Ensure your data systems are structured in a way that allows for efficient retrieval and complete deletion of an individual’s data across all relevant databases and third-party integrations. This is a significant technical challenge for many organizations.
- Train Staff: Provide comprehensive training to all customer-facing and data-handling staff on consumer rights, the process for handling requests, and the importance of compliance with the federal data privacy act.
Empowering consumers with greater control over their data is a core tenet of modern privacy legislation. Businesses that embrace these enhanced rights by building transparent and efficient processes will not only comply with the federal data privacy act but also build stronger, more trustworthy relationships with their customer base.
3. Stricter Data Security Requirements and Breach Notification
The 2026 federal data privacy act places a significant emphasis on data security, mandating stricter requirements for businesses to protect the personal data they collect and process. This goes beyond mere best practices; the act will likely require companies to implement specific technical and organizational measures designed to safeguard data against unauthorized access, disclosure, alteration, and destruction. While the exact prescriptive measures may vary, it is anticipated that the legislation will call for risk-based security assessments, encryption of sensitive data, access controls, regular security audits, and robust incident response plans. The goal is to shift the onus onto businesses to proactively secure data, rather than reacting only after a breach occurs.
Crucially, the act will also standardize and strengthen breach notification requirements. Currently, breach notification laws vary significantly by state, leading to confusion and inconsistencies. The federal data privacy act is expected to establish a clear, national standard for notifying affected individuals and relevant regulatory authorities in the event of a data breach. This will likely include specific timelines for notification (e.g., within 72 hours of discovery), details to be included in the notification, and thresholds for what constitutes a reportable breach. Non-compliance with these security and notification mandates will carry substantial penalties, underscoring the importance of a proactive and comprehensive security posture under the new federal data privacy framework.
What Businesses Need to Do:
- Conduct Regular Risk Assessments: Perform thorough and regular assessments of your data processing activities to identify and mitigate security risks to personal data. Document these assessments.
- Implement Robust Security Measures: Adopt industry-standard security practices, including encryption for data at rest and in transit, multi-factor authentication, access controls based on the principle of least privilege, and secure coding practices.
- Develop and Test Incident Response Plans: Create a detailed incident response plan that outlines steps to take in the event of a data breach, including containment, eradication, recovery, and communication. Regularly test this plan through simulations.
- Establish Clear Breach Notification Protocols: Familiarize yourself with the specific breach notification timelines and requirements of the federal data privacy act. Develop internal protocols to ensure timely and accurate notification to affected individuals and regulatory bodies.
- Vendor Security Management: Ensure that all third-party vendors and service providers who handle personal data on your behalf adhere to equivalent or higher security standards and have robust breach notification clauses in their contracts.
In an era of escalating cyber threats, strong data security is not just a compliance checkbox; it is fundamental to business resilience and customer trust. The 2026 federal data privacy act makes this an undeniable legal and ethical obligation.
4. Data Protection Impact Assessments (DPIAs) and Privacy by Design
The 2026 federal data privacy act is expected to embed the principles of ‘Privacy by Design’ and mandate ‘Data Protection Impact Assessments’ (DPIAs) for certain high-risk processing activities. Privacy by Design is a proactive approach, requiring businesses to integrate data protection and privacy considerations into the very core of their systems, services, products, and business practices from the outset, rather than as an afterthought. This means that privacy is not an add-on feature but an essential component of design and architecture. It encourages practices like data minimization, pseudonymization, and user control as default settings.
Complementing this, DPIAs will likely become a mandatory requirement for processing activities that are deemed likely to result in a high risk to the rights and freedoms of individuals. This could include large-scale processing of sensitive data, systematic monitoring of public areas, or the use of new technologies that involve novel forms of data collection. A DPIA is a process designed to identify and minimize the data protection risks of a project. It forces organizations to think critically about privacy implications before launching new products, services, or data processing operations. These requirements underscore a shift towards preventative measures and a more accountable approach to data handling under the federal data privacy act.
What Businesses Need to Do:
- Integrate Privacy by Design: Adopt a ‘privacy-first’ mindset in all stages of product development, system design, and service deployment. Ensure that privacy considerations are built into the architecture, rather than being patched on later.
- Establish DPIA Triggers: Develop clear criteria for when a DPIA is required. This typically includes processing sensitive data, large-scale data processing, systematic monitoring, and the use of new technologies.
- Conduct Thorough DPIAs: Implement a structured process for conducting DPIAs, involving relevant stakeholders (legal, IT, product development). The assessment should identify risks, propose mitigation strategies, and document the decision-making process.
- Document DPIA Findings: Maintain detailed records of all DPIAs, including the risks identified, the measures taken to mitigate those risks, and the rationale behind decisions. These documents will be crucial for demonstrating compliance with the federal data privacy act.
- Regularly Review and Update: DPIAs are not a one-time exercise. Regularly review and update existing DPIAs, especially when there are changes to data processing activities, technologies used, or legal interpretations.
Embracing Privacy by Design and conducting DPIAs are proactive steps that not only ensure compliance with the federal data privacy act but also lead to more secure, user-friendly, and trustworthy products and services. These practices demonstrate a commitment to ethical data stewardship.
5. Accountability and Governance: Data Protection Officers and Record Keeping
The 2026 federal data privacy act will likely usher in a new era of accountability and governance for businesses handling personal data. While the specifics may vary based on business size and data processing activities, it is highly probable that the act will mandate the appointment of a Data Protection Officer (DPO) for certain organizations. A DPO serves as an independent expert responsible for overseeing data protection strategy and implementation to ensure compliance with the act. They act as a point of contact for supervisory authorities and individuals regarding data protection matters, playing a critical role in fostering a culture of privacy within the organization.
Beyond the DPO, the act will undoubtedly impose stringent record-keeping obligations. Businesses will be required to maintain detailed records of their data processing activities, including categories of data processed, purposes of processing, categories of recipients, data retention schedules, and security measures implemented. This extensive documentation serves as proof of compliance and enables regulatory bodies to audit and verify adherence to the federal data privacy act. The emphasis here is on demonstrable accountability – companies must not only comply but also be able to prove their compliance through meticulous record-keeping and robust governance structures. This shift demands a more formalized and integrated approach to data privacy within an organization’s overall governance framework.
What Businesses Need to Do:
- Assess DPO Requirement: Determine if your business is required to appoint a Data Protection Officer based on the act’s criteria (e.g., scale of data processing, nature of data). If so, appoint an individual with expert knowledge of data protection law and practices.
- Define DPO Responsibilities: Clearly define the DPO’s role, responsibilities, and reporting lines to ensure their independence and effectiveness. The DPO should have direct access to the highest management level.
- Implement Comprehensive Record-Keeping: Establish systems and processes to maintain accurate and up-to-date records of all data processing activities. This includes data inventories, processing purposes, data sharing agreements, consent records, DPIAs, and breach notifications.
- Develop Internal Policies and Procedures: Create and regularly update internal policies and procedures for data handling, employee training, data access, and incident management to reflect the requirements of the federal data privacy act.
- Conduct Regular Audits and Reviews: Periodically audit your data protection practices and records to ensure ongoing compliance and identify areas for improvement. This demonstrates a commitment to continuous improvement in data governance.
Strong accountability and robust governance are the backbone of effective data privacy. By establishing clear roles, maintaining diligent records, and fostering a culture of privacy, businesses can confidently meet the demands of the 2026 federal data privacy act and build enduring trust with their stakeholders.
Preparing Your Business for the Future of Federal Data Privacy
The impending 2026 federal data privacy act represents a significant evolution in the regulatory landscape, one that demands proactive and strategic engagement from every business handling personal data. The five key compliance changes discussed – the expanded definition of personal data, enhanced consumer rights, stricter data security, mandatory DPIAs and Privacy by Design, and robust accountability and governance – are not isolated requirements but interconnected components of a comprehensive data protection framework. Ignoring or delaying preparation for these changes is a perilous path that could lead to substantial penalties, legal challenges, and irreparable damage to your brand’s reputation.
Beyond mere compliance, embracing these new federal data privacy standards offers a unique opportunity for businesses to differentiate themselves. In an increasingly privacy-conscious world, companies that demonstrate a genuine commitment to protecting customer data will gain a competitive edge. This commitment translates into increased customer loyalty, enhanced brand perception, and a stronger foundation for sustainable growth. It’s about building trust in an age where trust is a valuable currency.
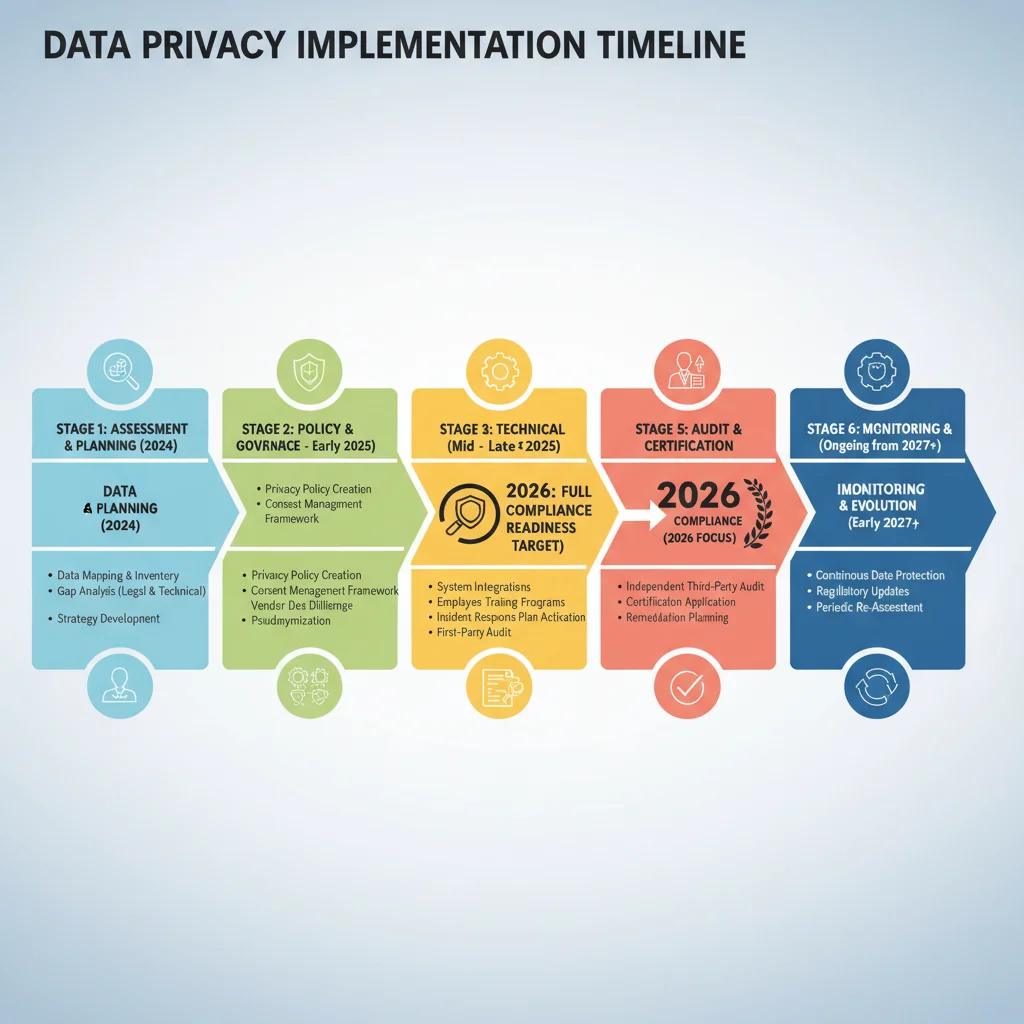
The journey to full compliance with the 2026 federal data privacy act will require a multi-faceted approach, involving legal, technical, and operational adjustments. It is not a task for a single department but a collaborative effort across the entire organization. From the executive board setting the strategic direction to IT implementing secure systems, legal advising on compliance, and marketing ensuring transparent communication, every part of your business has a role to play. Investing in expert legal counsel, advanced technological solutions, and comprehensive employee training will be crucial for a smooth transition.
Consider conducting a thorough gap analysis now to identify where your current practices fall short of the anticipated federal requirements. Develop a detailed roadmap with clear timelines, assigned responsibilities, and measurable milestones. Regular internal audits and reviews will be essential to track progress and ensure ongoing adherence. Remember, compliance is not a one-time event but an ongoing commitment to responsible data stewardship. The 2026 federal data privacy act is not just another regulation; it’s a call to action for businesses to prioritize privacy as a core business value.
By proactively addressing these five key compliance changes, your business can transform potential challenges into significant opportunities, ensuring not only legal adherence but also fostering deeper trust with your customers and securing a resilient future in the evolving digital economy. The future of federal data privacy is here, and preparedness is paramount.